DO YOU KNOW IF YOUR COMPANY IS REALLY GDPR COMPLIANT?
Many companies have the basic documentation in place, but that alone does not mean their processing of personal data complies with the law.
The most common challenges include:
- incomplete records of processing activities,
- unclear retention periods,
- outdated agreements with data processors,
- missing personal data protection controls and procedures,
- insufficient oversight of personal data processing,
- difficulty demonstrating compliance during regulatory inspections.
Mikrocop helps you establish the right processes, documentation and organizational measures so that you can also demonstrate personal data protection compliance.
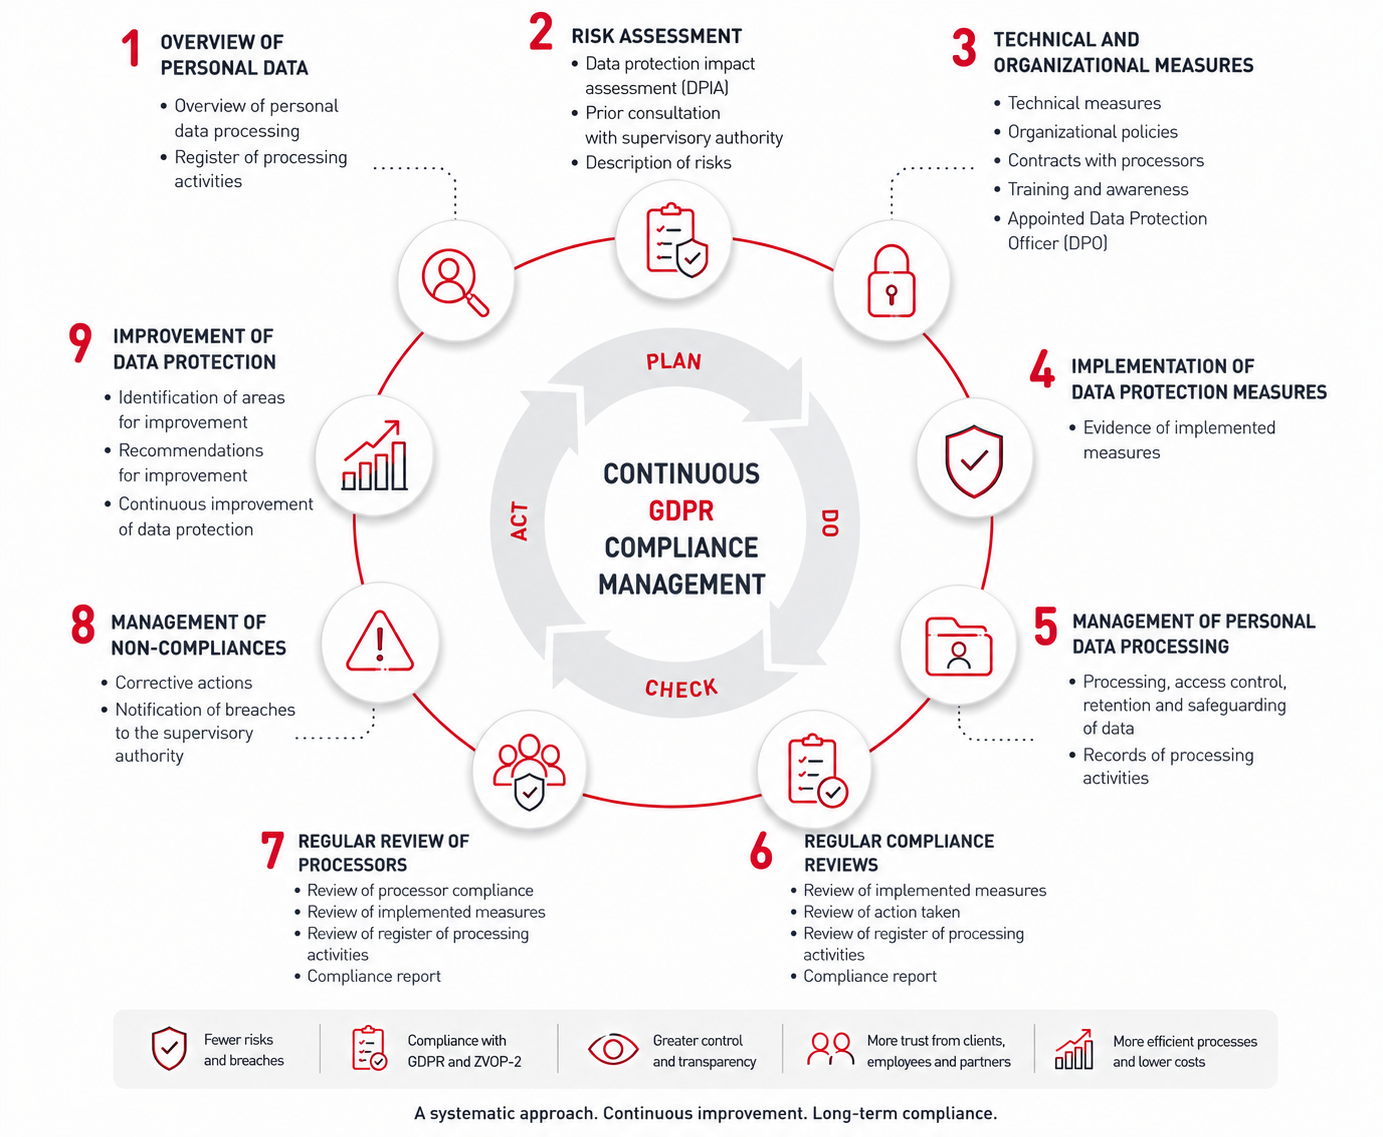
STEPS TO ENSURE DATA PROTECTION COMPLIANCE

PLAN
- Overview of data filing systems
- Identification of risks
- Personal data protection

DO
- Implementation of personal data protection measures
- Processing of personal data

CHECK
- Verification of data management compliance
- Regular audits of outsourced processors

ACT
- Resolving issues of non-compliance
- Preventing recurrence of non-action and improving protection
YOUR BENEFITS
With a comprehensive approach to personal data protection, we help you achieve and maintain compliance with the GDPR and ZVOP-2. We ensure that your processes, documentation and organizational measures are aligned with legal requirements and adapted to the way your company actually operates.
- A clear overview of personal data processing.
- Reduced risk of data protection breaches.
- Well-organized GDPR documentation.
- Better preparedness for regulatory inspections.
- Appropriately defined retention periods.
- Greater trust among employees and business partners.
GDPR COMPLIANCE IS AN ONGOING PROCESS, NOT A ONE-OFF TASK
WHY DO COMPANIES CHOOSE MIKROCOP?
Interdisciplinary expertise
Our experts combine knowledge of personal data protection, document management, information security and regulatory compliance. This enables us to provide comprehensive consulting services.
Long-term support
Our support does not end once the initial compliance work is complete. Where required, we can also act as your external DPO and help you maintain compliance as legislation, business processes and information systems evolve.
Proven methodology
Our consulting is based on proven methodologies that enable a systematic approach to personal data processing and support long-term compliance with the GDPR and ZVOP-2.
SUCCESS STORIES
We began aligning our personal data protection practices with a gap analysis. We effectively addressed the identified gaps and adapted to the requirements of the GDPR in time, while also using the compliance process to identify opportunities for digitalization.– Boris Šušmak, Luka Koper
FREQUENTLY ASKED QUESTIONS
How do we know whether our company is GDPR compliant?
GDPR compliance depends not only on having the required documentation in place, but above all on how personal data is processed in practice and which controls your company has implemented and actually applies. At Mikrocop, we first review your personal data processing activities, existing documentation, and technical and organizational measures, and identify potential risks. Based on the analysis, we prepare a clear action plan to help your company progressively align its practices with the requirements of the GDPR and ZVOP-2.
What does GDPR compliance consulting include?
Our consulting covers the entire compliance process – from reviewing personal data processing activities and conducting a gap analysis to preparing the necessary documentation, records of processing activities, and recommendations for technical and organizational measures. Where required, we also review agreements with data processors and advise you on maintaining compliance over the long term.
Does every company need to maintain records of processing activities?
Records of processing activities are a key GDPR requirement for many companies and organizations. Whether they are mandatory depends on the nature and scope of personal data processing, but maintaining such records is also advisable where they are not explicitly required. They provide a clear overview of what personal data you process, for what purposes, how long it is retained and who has access to it.
Do we need a Data Protection Officer (DPO)?
Not every company is required to appoint a Data Protection Officer. Whether this obligation applies depends on the nature of the organization's activities and the scope of its personal data processing. If you are unsure whether you need to appoint a DPO, we can assess your obligations as part of our consulting services and help you determine the most appropriate solution for your organization.
What is a gap analysis and why is it important?
A gap analysis is the first step towards achieving GDPR compliance. It compares the current situation in your company with applicable legal requirements and identifies areas that need to be addressed or improved. The result is a clear overview of the required actions, priorities and recommendations for achieving compliance efficiently, without unnecessary costs or duplicated work.
Do you also review agreements with data processors?
Yes. The GDPR requires companies to work with data processors on the basis of appropriately structured agreements. We review whether these agreements contain all legally required elements, clearly define the responsibilities of both parties and provide an appropriate level of personal data protection.
Is GDPR compliance a one-off project or an ongoing process?
GDPR compliance is not a one-off project, but an ongoing process. Organizations introduce new information systems, change business processes, enter into agreements with new partners and begin processing new categories of personal data. This is why compliance needs to be reviewed regularly, documentation kept up to date, and technical and organizational measures adapted to new requirements and risks.
Do you know if your company is really GDPR compliant?
Schedule an initial consultation. Together, we will review your current situation, identify potential risks and prepare recommendations for the next steps.
MORE FROM MIKROCOP
Ensure compliance with GDPR and ZVOP-2 without unnecessary risks
Blog

We protect personal data all the time or not at all
If we have only implemented the most critical adaptations to personal data protection systems, it is now high time to define the long-term strategy. Personal data protection is not a state we reach but a live and dynamic process that must be monitored, optimized and supervised all the time.
Blog

If we really want to protect personal data, we have to take comprehensive care of it
Ensuring compliance of personal data protection with the GDPR is a pressing issue for all who deal with personal data on a daily basis as data controllers or data processors.
Blog
Personal data protection is an ongoing concern
Data protection compliance is not a project we complete and then put aside on a shelf. Quite the contrary, it is a journey that never really ends.


